
Operating System
Cyber threats evolve daily, but internal safeguards remain your first line of defense. These 10 proven strategies empower cybersecurity leaders to build resilient data protection frameworks that adapt to modern risks while aligning with business operations.
Role-Based Access Control Implementation
Think of your company’s data like a high-security vault—every employee shouldn’t have the master key. Role-Based Access Control (RBAC) ensures only the right people access what they need to do their jobs, nothing more. This isn’t just about locking doors; it’s about eliminating accidental exposure risks by design. For example, a marketing team member shouldn’t access payroll files, and a developer shouldn’t modify HR records—even if they’re curious (or mistaken).
Modern RBAC systems like Microsoft Azure AD or Okta go beyond simple user groups. They integrate with attribute-based access controls (ABAC), letting you set rules like "only finance staff can view Q3 revenue reports between 9 AM and 5 PM." Audit logs track every access attempt, so you’ll spot anomalies before they become breaches. The result? A 70% reduction in insider risk while keeping workflows smooth.
This safeguard is a must for regulated industries (healthcare, finance) but pays off anywhere sensitive data lives. Start by mapping roles to data assets—then enforce least-privilege access company-wide. Your data (and sanity) will thank you. 💻
Multi-Factor Authentication Enforcement
Passwords alone are like leaving your front door unlocked—even if it’s a sturdy door, determined attackers will find a way in. Multi-Factor Authentication (MFA) adds that critical second layer, requiring a second verification (like a fingerprint, security token, or one-time code) after the password. This simple step blocks 99.9% of automated attacks while keeping legitimate users logged in with minimal friction.
Modern MFA solutions like Microsoft Authenticator or Duo Security integrate seamlessly with SSO platforms (Okta, Azure AD) and support biometric, hardware token, or push-notification methods. The best part? You can enforce MFA for high-risk departments (finance, R&D) without disrupting workflows—employees get a one-tap approval on their phones, while attackers face an insurmountable hurdle. Even better, FIDO2 keys eliminate phishing risks by storing credentials locally.
This isn’t just for big enterprises—remote teams or SMBs handling sensitive data (like healthcare providers or legal firms) see immediate ROI. Start with critical accounts (admin, finance, HR) to test the impact before rolling it out company-wide. 💻
Automated Data Classification Tools
Tired of sifting through spreadsheets to find sensitive data? Automated data classification tools use AI to scan and tag records—like credit card numbers or medical histories—automatically, so you can enforce policies without manual tagging.
Solutions like Microsoft Purview or Varonis analyze content in real-time, flagging PII, financial docs, and contracts with 95%+ accuracy. They integrate with existing systems (SharePoint, OneDrive) and adapt to new data types, cutting compliance risks by up to 70%.
Perfect for legal, healthcare, or finance teams where misclassification could trigger fines. These tools turn reactive security into proactive protection. ⚡
Endpoint Detection and Response Deployment
Zero-day exploits don’t announce themselves—and neither should your detection systems. Endpoint Detection and Response (EDR) solutions like CrowdStrike or SentinelOne provide real-time behavioral monitoring to flag suspicious activity before it spreads across devices.
These tools analyze fileless malware, unusual process chains, and lateral movement attempts with sub-second response times. Unlike traditional antivirus, EDR correlates device-level events across your entire network, even on BYOD laptops or remote workstations. Automated containment isolates threats without manual intervention, while forensic reports help security teams trace attack origins.
Perfect for hybrid teams or organizations with mixed device fleets, EDR turns reactive security into a proactive shield. 💪
Regular Security Awareness Training Programs
Your strongest defense isn’t firewalls—it’s the people behind them. 90% of breaches start with human error, and AI-driven phishing attacks now mimic real conversations with eerie accuracy, tricking even seasoned employees. That’s why interactive training programs with simulated attacks and real-time feedback are non-negotiable for modern workplaces.
Look for platforms that combine quarterly phishing simulations (like KnowBe4’s AI-powered attack simulations) with gamified modules that reward employees for spotting threats. These programs adapt to new attack vectors—like deepfake voice scams or malicious PDFs—and provide instant coaching when mistakes happen. The goal isn’t perfection; it’s building muscle memory so employees recognize red flags before they click.
This safeguard pays off most for remote-first teams or industries handling sensitive data (healthcare, finance). Start with a pilot program for high-risk departments, then scale based on engagement metrics. 💡
Immutable Backup and Recovery Systems
When ransomware locks your files, traditional backups become useless if they’re connected to the same network. Immutable backup systems solve this by storing copies in physically isolated (air-gapped) environments—unreachable by cybercriminals—while retaining versioned snapshots to restore data to any point in time.
Solutions like Veeam or Commvault combine WORM (Write Once, Read Many) storage with automated, encrypted backups to critical cloud or on-premise vaults. The key is unalterable recovery points: even if an attacker encrypts your primary systems, you can restore from a pre-infection snapshot without paying ransom. For healthcare or finance, this means compliance-ready recovery with minimal downtime.
This isn’t just for enterprises—small businesses with critical operations (like law firms or manufacturing) can deploy hybrid air-gapped solutions (e.g., USB drives stored offsite) for under $500/month. The peace of mind alone makes it worth the investment. ✨
Network Segmentation Architecture
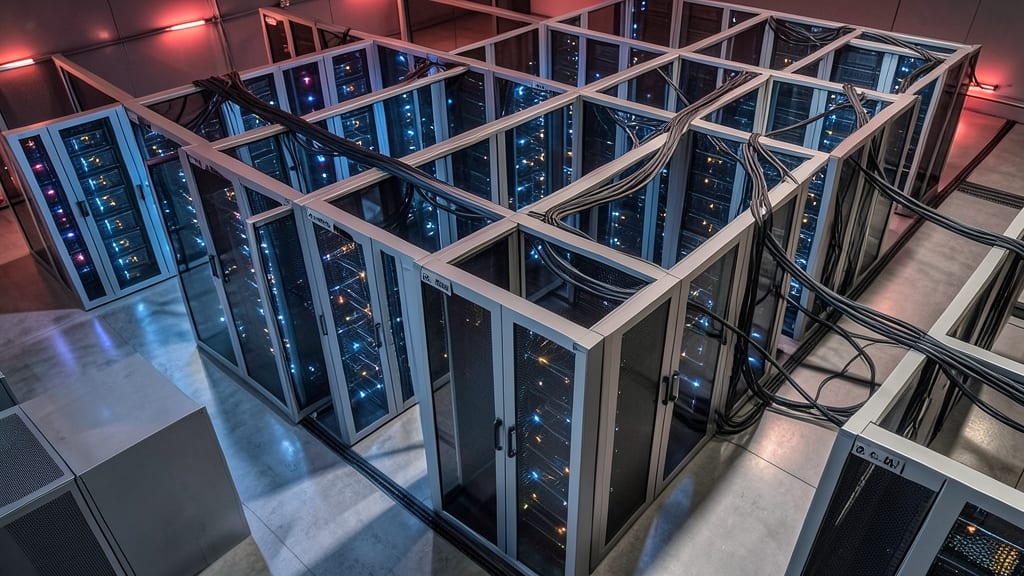
Imagine a breach slipping past your firewalls—now picture it hitting a dead end because your HR servers are isolated from finance systems. That’s the power of network segmentation: turning your entire infrastructure into a digital maze where attackers can’t easily move laterally.
By dividing networks into department-specific zones (e.g., VLANs for IT, DMZs for public-facing apps), you limit an intruder’s access to only the segment they’ve compromised. Tools like Cisco ACI or Juniper SRX automate this with zero-trust policies, ensuring even privileged users can’t jump between segments without explicit approval. The result? Contained damage—no single breach becoming a full-scale disaster.
This approach is non-negotiable for regulated industries (healthcare, finance) but also a game-changer for SMBs with hybrid cloud setups. Start with critical departments like payroll or R&D to test the impact. ✨
Privileged Access Management Solutions
Tired of permanent admin accounts lingering like digital ghosts in your infrastructure? Privileged Access Management (PAM) solutions eliminate this risk by granting elevated permissions only when—and for as long as—they’re needed.
With just-in-time (JIT) access, tools like CyberArk or BeyondTrust let DevOps teams or contractors spin up temporary admin rights for specific tasks, then automatically revoke them. Features like session recording and multi-factor authentication ensure accountability, while automated credential rotation prevents credential stuffing attacks. For example, a contractor fixing a server issue gets access for exactly 30 minutes—no lingering privileges.
This approach is perfect for DevOps pipelines or contractors who need elevated access without creating permanent vulnerabilities. It’s the digital equivalent of a time-locked safe—secure by design. ✨
Incident Response Playbooks for Critical Scenarios
When a breach hits, every minute counts—and Incident Response Playbooks turn chaos into structured action. These predefined guides map out exact steps for ransomware containment, data leak mitigation, or insider threat investigations, ensuring your team responds faster than attackers can escalate damage.
Think of them as battle-tested checklists for crises: isolating infected systems, notifying stakeholders, and preserving evidence—all while minimizing compliance violations. Tools like Splunk’s IR playbooks or IBM’s Resilient platform integrate with SIEM systems to automate initial triage, reducing human error during high-pressure moments.
Ideal for regulated industries (healthcare, finance) or any team handling sensitive data, these playbooks transform reactive scrambling into predictable, repeatable defense. ⚡
Third-Party Risk Assessment Frameworks
Your company’s security chain is only as strong as its weakest third-party link. A single vendor with outdated encryption or unpatched systems can turn your entire data protection strategy into a backdoor for attackers—yet many organizations overlook this critical blind spot.
Third-party risk assessment frameworks like NIST SP 800-161 or ISO/IEC 27005 provide structured methodologies to evaluate partners, contractors, and SaaS tools. Automated tools such as OneTrust Vendorpedia or Prevalent streamline quarterly audits, scoring vendors on compliance gaps, incident histories, and security maturity. These frameworks force you to ask: Does this vendor’s security match ours? before granting access to your systems.
Ideal for enterprises with sprawling ecosystems (think cloud providers, payroll processors, or freelance developers), these frameworks turn vendor risk from a reactive nightmare into a proactive safeguard. 💪